• Skip to primary navigation
  • Skip to main content
  • Skip to primary sidebar
  • Skip to footer
Sq Magazine LogoSQ Magazine

Smarter Insights for a Fast-Moving Digital World

  • Latest News
  • Statistics
  • Tools
  • About
  • Contact
  • Subscribe
Subscribe
Sq Magazine Logo
  • Latest News
  • Statistics
  • Tools
  • About
  • Contact
Add as a preferred
source on Google
Home » Cybersecurity

ModSecurity Upload Bypass Exploit Goes Public With No Patch Listed

Published on: November 9, 2026, 9:02 AM EST
Sofia Ramirez
Senior Tech Writer • 699 Articles
Sofia Ramirez is a technology and cybersecurity writer at SQ Magazine. With a keen eye on emerging threats and innovations, she helps reader...
LATEST POSTS:
SEC Philippines Confirms Data Breach on Digital Platforms
ModSecurity Upload Bypass Exploit Goes Public With No Patch Listed
Drone Statistics 2026: Registrations, Pilots and Commercial Fleets
Robert A. Lee
Senior Editor • 473 Articles
Robert A. Lee is a journalist at SQ Magazine who unpacks the fast-moving worlds of gaming and internet trends. He tracks everything from maj...
LATEST POSTS:
Yelp Statistics 2026: Reviews, Revenue and Advertiser Base
Education Technology Trends: What Holds Up in 2026
Anthropic Files S-1 for Nasdaq IPO Under Symbol ANT
Modsecurity Waf Flaw
As Featured In
The New York Times LogoForbes LogoWired LogoDeloitte LogoResearch.com Logo
Share on LinkedIn ChatGPT Perplexity Share on X Share on Facebook

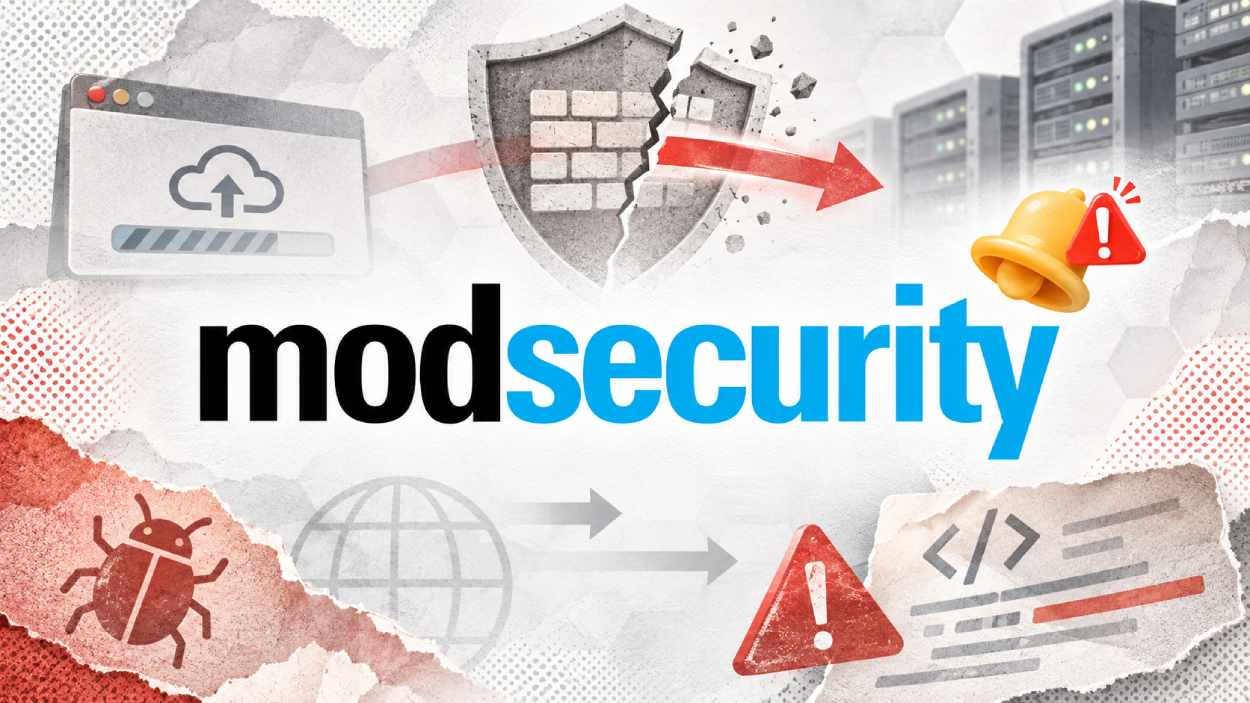
HKCERT warned on 9th November, 2026 that proof-of-concept exploit code is public for CVE-2026-104269, a ModSecurity upload bypass with no patched version listed. The bug lets a file named like a JPG reach the app as a PHP script.

At a Glance

  • HKCERT rated CVE-2026-104269 a Medium Risk security restriction bypass and flagged public proof-of-concept exploit code.
  • ModSecurity versions 3.0.0 and later carry the filename bug, and its GitHub advisory lists no patched release.
  • Go, Python, Node.js, and Java Spring parsers can read a different filename than the one the firewall checked.
  • A second bug, CVE-2026-73857, hits 3.0.15, 3.0.16, and the v3 master only when SecParseXmlIntoArgs is switched on.

ModSecurity checks one filename, the app saves another

ModSecurity is the open-source web application firewall (WAF) that runs with Apache, IIS, and Nginx and blocks requests that look harmful. Its weak spot here is the multipart parser, the code that reads file uploads. That parser doesn’t support RFC 2231, a standard for encoded values in headers.

Many app frameworks do support it. When an upload carries both a plain filename and an encoded filename*, those frameworks prefer the encoded one. The WAF and the backend end up reading two different names from one request.

The attack is short. An attacker sends filename=”safe.jpg” together with filename*=UTF-8”shell.php, and the OWASP Core Rule Set sees a harmless JPG and lets it through. A Go backend reads the name as shell.php and may save it to disk. If the web server serves that folder, the attacker can run code on it.

The bulletin from HKCERT (Hong Kong’s computer emergency response team) frames the damage around what the app does with that name. Apps that use the backend-selected name for storage, extension checks, or content-type inference “can therefore receive a filename that bypassed WAF inspection,” the bulletin said.

The GitHub advisory, GHSA-5pww-8rfg-9crf, names Go, Python (Flask and FastAPI), Node.js, and Java Spring parsers as the ones that behave this way. PHP’s native upload handling reads only filename=, so it isn’t affected. Researchers 0xkalawy and ZeyadZonkorany found the issue, and B0YK4 coordinated the report.

The XML bug needs a non-default switch

Maintainer airween published both GitHub advisories on September 30. The second, CVE-2026-73857 (GHSA-jx3r-phvx-2jmj), came from researcher Tobias Klein. A single crafted request from an unauthenticated remote user can push a worker process into using an uninitialized pointer. That request can then write a fixed value to an address the sender picks.

The fallout ranges from a crash or memory leak to a redirect of program flow, which could lead to remote code execution. The advisory lists the weaknesses as CWE-787 (out-of-bounds write) and CWE-824 (access of uninitialized pointer).

Exposure is narrow, though. The bug is reachable only when SecParseXmlIntoArgs is set to On or OnlyArgs, and the setting ships Off by default. The code path arrived in 3.0.15, so 3.0.15, 3.0.16, and the current v3 master are affected. Earlier 3.0.x releases and ModSecurity v2 are not.

Patch status for this one is muddled. The advisory lists 3.0.17 as the patched version. Yet its text also says a fix is “not yet” available and will come in the next release.

Exploit code lands before the upload fix

HKCERT’s note changes the math on the filename bug more than on the XML one. CVE-2026-104269 needs no login, reaches every release from 3.0.0 onward, and now has public exploit code, while its advisory still lists no fix. The XML bug, by contrast, sleeps unless an admin turned a specific setting on.

The upload bypass also defeats WAF-side extension filtering. A rule can’t block shell.php when the firewall never sees that name, so the backend’s own handling becomes the real control.

Teams running ModSecurity in front of Go, Python, Node.js, or Java Spring apps can reduce risk with these general hardening steps:

  • Ignore the client-supplied filename and generate a safe name on the server.
  • Block script extensions such as .php at the application layer.
  • Store uploads outside the web root, so the web server doesn’t serve them directly.
  • Confirm SecParseXmlIntoArgs is set to Off, the workaround from the CVE-2026-73857 advisory.
Newsletter
Don’t chase tech news. We track it for you.

One weekly briefing with the launches, AI developments, and breaches that matter. No filler.

Read by pros at Fortinet, TSMC, Barclays, and Deloitte.

What’s Next?

Two questions sit open in the public record. When will a release fix CVE-2026-104269? And does 3.0.17 actually ship the XML fix, given the advisory’s conflicting text?

The next marker for admins is that 3.0.17 release on the official ModSecurity project page. Until it lands and the notes confirm the XML fix, SecParseXmlIntoArgs stays Off and upload names stay server-generated.
Definition of AI Inference. Link to full glossary entry follows the description.AI Inference

AI inference is the execution phase where a trained AI model applies what it learned to new, unseen data and produces an output such as a prediction.

Read more about AI Inference

This article has been reviewed and fact-checked by Robert A. Lee. SQ Magazine follows strict Publishing Principles and a documented Fact-Check Policy to ensure accuracy, transparency, and editorial independence across all content.

Add SQ Magazine as a Preferred Source on Google for updates! Follow on Google News
Share ChatGPT Perplexity

References

  • HKCERT: ModSecurity Security Restriction Bypass Vulnerability
Sofia Ramirez

Sofia Ramirez

Senior Tech Writer


Sofia Ramirez is a technology and cybersecurity writer at SQ Magazine. With a keen eye on emerging threats and innovations, she helps readers stay informed and secure in today’s fast-changing tech landscape. Passionate about making cybersecurity accessible, Sofia blends research-driven analysis with straightforward explanations; so whether you’re a tech professional or a curious reader, her work ensures you’re always one step ahead in the digital world.

Related Posts

Windows Paint Patch Store
Cybersecurity

Microsoft Paint RCE Fix Lands in Store, Not Windows Update

Openssh Alpine Linux Flaw Patch
Cybersecurity

OpenSSH Fixes Critical Long-Password Bypass on Alpine Linux

Elevenlabs And Soundcloud Partnership Ai Music
Artificial Intelligence

ElevenLabs Adds Direct SoundCloud Publishing for AI Music

Disclaimer: The content published on SQ Magazine is for informational and educational purposes only. Please verify details independently before making any important decisions based on our content.

Reader Interactions

Leave a Comment Cancel reply

Primary Sidebar

Connect With Us

facebook x linkedin google-news telegram pinterest whatsapp email
google-preferred-source-badge Add as a preferred source on Google

You Should Also Read

Debian and Ubuntu Patch APT Flaw That Hands Attackers Root
DreamHost Confirms Hackers Stole Session Tokens and Logins
How Public Records Sites Expose You to Identity Theft and Doxxing

Table of Contents

  • At a Glance
  • ModSecurity checks one filename, the app saves another
  • The XML bug needs a non-default switch
  • Exploit code lands before the upload fix
  • What’s Next?

Weekly stats quiz Week 46

How much of a tech geek are you?

5 fast questions from this week's verified industry data. About a minute.

Play the quiz New every Monday

Footer

SQ Magazine Logo

Smarter Insights for a Fast-Moving Digital World

Connect With Us

Follow Us on Google News

Editorial & Trust

  • About
  • Publishing Principles
  • Fact-Check Policy
  • Corrections Policy
  • Ethics Policy
  • Disclaimer
  • Cookie Policy

Worth Checking

  • The Tech Index
  • The Threat Index
  • Social Media Attention Span Stats
  • Instagram Followers Stats
  • Google Usage Stats
  • LLM Hallucination Stats
  • Gen Z Social Media Stats
Contact Us
13570 Grove Dr #189,
Maple Grove, MN 55311,
United States
10 a.m. to 6 p.m. | Every day

Copyright © 2022–2026 SQ Magazine. All Rights Reserved. Powered by the Neural Stack.

  • Privacy Policy
  • Terms
  • Accessibility Statement
Company
  • About Us
  • Our Team
  • Our Mission
  • Core Values
Discover
  • Brand Assets
    Brand Assets
  • Stats Methodology
    Stats Research Process
  • Glossary
    Glossary
Categories
  • Internet
  • Technology
  • Artificial Intelligence
  • Gaming
Internet
Yelp Statistics 2026: Reviews, Revenue and Advertiser Base
Influencer Marketing Platform Statistics 2026: Market and Spend
Dailymotion Statistics Users Views and Market Share
Dailymotion Statistics 2026: Users, Views and Market Share
Average Attention Span Statistics The Cross-Domain Numbers
Average Attention Span Statistics 2026: The Cross-Domain Numbers
How Many Videos Are on YouTube Statistics
How Many Videos Are on YouTube Statistics 2026: Key Data
How Many People Work at WhatsApp
How Many People Work at WhatsApp 2026: Employee Count and History
Technology
Drone Statistics Registrations Pilots and Commercial Fleets
Drone Statistics 2026: Registrations, Pilots and Commercial Fleets
RevenueCat Statistics Apps Revenue and Market Share
RevenueCat Statistics 2026: Apps, Revenue and Market Share
Linux Distro Market Share Statistics Most Popular Distributions
Linux Distro Market Share Statistics 2026: Most Popular Distributions
Average US Salary Statistics Median Income by Age and State
Average US Salary Statistics 2026: Median Income by Age and State
Aptoide Statistics 2026: Downloads, Users and App Store Share
AppsFlyer Statistics Customers Revenue and Market Position
AppsFlyer Statistics 2026: Customers, Revenue and Market Position
Artificial Intelligence
NotebookLM Statistics Users Growth and Adoption
NotebookLM Statistics 2026: Users, Growth and Adoption
Cursor AI Statistics 2026: Users, Revenue and Developer Adoption
AI Search Engine Statistics Usage Market Share and Adoption
AI Search Engine Statistics 2026: Usage, Market Share and Adoption
AI Music Statistics
AI Music Statistics 2026: Generation, Adoption and Industry Impact
AI Coding Statistics
AI Coding Statistics 2026: Adoption, Productivity and Market Data
How Much Content on Social Media Is AI Generated Statistics
How Much Content on Social Media Is AI Generated Statistics 2026: Hidden Truths
Gaming
Clash Royale Statistics Revenue Players and Engagement
Clash Royale Statistics 2026: Revenue, Players and Engagement
Gaming Statistics
Gaming Statistics 2026: Market Size, Players, Revenue, and Platforms
Roblox vs Minecraft Statistics
Roblox vs Minecraft Statistics 2026: Players, Revenue, Creators
Online Gambling Regulations Statistics
Online Gambling Regulations Statistics 2026: Global Compliance and Enforcement Data
Fantasy Sports Statistics
Fantasy Sports Statistics 2026: Users, Revenue & Trends
Apex Legends Statistics 2026: Players, Revenue, and Esports
Categories
  • Artificial Intelligence
  • Cybersecurity
  • Technology
  • Internet
Artificial Intelligence
Claude Fable Mythos 5 2 Launch
Anthropic Unleashes Fable 5.2, Keeps Mythos Restricted
Elevenlabs And Soundcloud Partnership Ai Music
ElevenLabs Adds Direct SoundCloud Publishing for AI Music
Chatgpt Work Codex Limits
ChatGPT and Codex to Share Usage Limits as Work Tab Merges
Nvidia Nemotron 3 5 Transcribe Model
Nvidia Releases Open Nemotron 3.5 Transcribe Model for 40 Languages
Google Deepmind Genie 4 Adds Native Audio And Live Scene
Google DeepMind Genie 4 Adds Native Audio and Live Scene Edits
Anthropic European Consultancy Firms
Anthropic and Hg to Launch AI Consultancy for European Firms
Cybersecurity
Sec Philippines Data Breach Confirmation
SEC Philippines Confirms Data Breach on Digital Platforms
Modsecurity Waf Flaw
ModSecurity Upload Bypass Exploit Goes Public With No Patch Listed
Windows Paint Patch Store
Microsoft Paint RCE Fix Lands in Store, Not Windows Update
Openssh Alpine Linux Flaw Patch
OpenSSH Fixes Critical Long-Password Bypass on Alpine Linux
Ubuntu Debian Apt Patch Fix
Debian and Ubuntu Patch APT Flaw That Hands Attackers Root
Dreamhost Data Breach Confirmed
DreamHost Confirms Hackers Stole Session Tokens and Logins
Technology
Apple App Store Romantic Ai Apps Removal
Apple Moves Romantic AI Companions and Dating Apps to 18+
Amazon Echo Time Smart Device Launch
Amazon Unveils Echo Time: A Smarter Alarm Clock
Arc Browser Shutdown Confirmed
The Browser Company Will Shut Down Arc on December 22
Spotify Family Plan Qr Sharing
Spotify Adds QR Checks to Verify Family Plan Households
Apple Music New Logo Rebrand
Apple Music Rebrands With a Logo Made by Fred Again’s Music
Apple Homepod Mini 2 Preorder Featured 1
Apple Launches HomePod Mini 2 with £149 and Opens Pre-Order
Internet
Anthropic Files S 1 Ipo With Sec
Anthropic Files S-1 for Nasdaq IPO Under Symbol ANT
Microsoft 365 Family Sharing Storage Cuts
Microsoft 365 Family Faces Massive OneDrive Storage Cut
Meta Launched Meta One Subscription
Meta One Bundles Instagram, Facebook, WhatsApp Into One AI Subscription
Apple Wallet Ids Launch In Oklahoma
Apple Wallet IDs Launch in Oklahoma in Major Expansion
Meta to Pay 18 Billion in Landmark Teen Safety Deal
Meta to Pay $18 Billion in Landmark Teen Safety Deal
Whatsapp Brings Passkeys 2fa
WhatsApp Hits 1 Billion Passkey Users, Adds 2FA Passwords
Security Calculators
  • Random Password Generator Strong random passwords, with the strength of each shown.
  • Uptime Calculator Downtime an uptime target allows, from a day to a year.
  • Download Time Calculator How long a file takes at your connection speed.
Network Tools
  • What Is My IP Address Your public IP, provider and location, read at the edge.
  • IP Subnet Calculator Network, broadcast, host range and mask for any IPv4 block.
  • What Is My User Agent What a user agent string says about the browser behind it.
  • What Is My Screen Resolution Your screen size, pixel ratio and viewport, read live.
  • TXT Record Lookup TXT, SPF and DMARC records for any domain.
All 8 Network Tools
AI Tools
  • Token Counter Token counts for GPT-4o and GPT-4 encodings.
All 12 tools
Newsletter

Too much tech noise?

We respect your time. One high-signal briefing a week: tech, AI, and security. Nothing else.

Read by pros at Fortinet, TSMC, Barclays, and Deloitte.