• Skip to primary navigation
  • Skip to main content
  • Skip to primary sidebar
  • Skip to footer
Sq Magazine LogoSQ Magazine

Smarter Insights for a Fast-Moving Digital World

  • Latest News
  • Statistics
  • About
  • Contact
Subscribe
Sq Magazine Logo
  • Latest News
  • Statistics
  • About
  • Contact
Subscribe
Home » Cybersecurity

Palo Alto Networks Patches 13 PAN-OS Vulnerabilities

Published on: July 9, 2026, 2:37 PM EDT
Sofia Ramirez
Written By
Sofia Ramirez
Sofia Ramirez
Senior Tech Writer • 617 Articles
Sofia Ramirez is a technology and cybersecurity writer at SQ Magazine. With a keen eye on emerging threats and innovations, she helps reader...
LATEST POSTS:
Aptoide Statistics 2026: Downloads, Users and App Store Share
YouTube’s AI Feed Builder Changes Video Discovery
Arista VeloCloud Flaw Hits CVSS 10.0: Patch Now
Robert A. Lee
Reviewed By
Robert A. Lee
Robert A. Lee
Senior Editor • 456 Articles
Robert A. Lee is a journalist at SQ Magazine who unpacks the fast-moving worlds of gaming and internet trends. He tracks everything from maj...
LATEST POSTS:
Top 10 Dynamics 365 Partners in the UK for 2026
Meta One Bundles Instagram, Facebook, WhatsApp Into One AI Subscription
How Many Videos Are on YouTube Statistics 2026: Key Data
Palo Alto Networks Patches 13 Pan Os Vulnerabilities
As Featured In
The New York Times LogoForbes LogoWired LogoDeloitte LogoResearch.com Logo
Share on LinkedIn ChatGPT Perplexity Share on X Share on Facebook

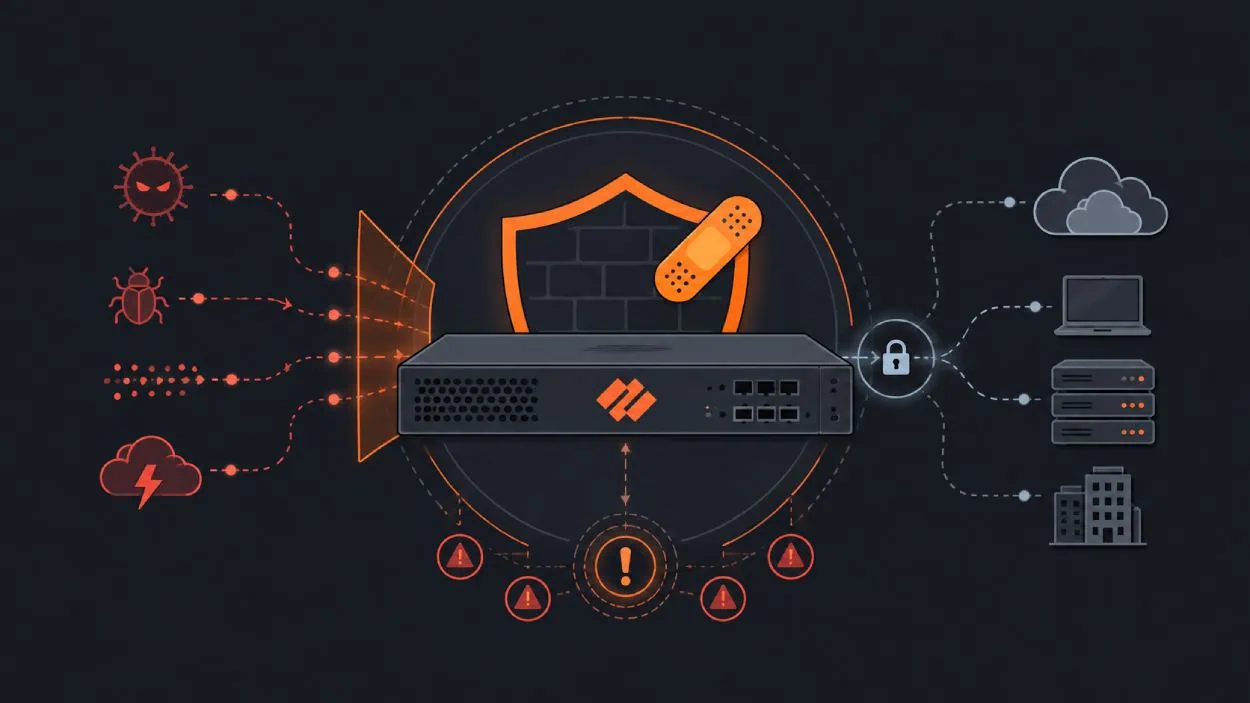
Palo Alto Networks published a security advisory on July 8, 2026, for CVE-2026-0288, a high-severity, highest-urgency buffer overflow in the PAN-OS firewall software. The advisory is one of 13 vulnerabilities Palo Alto Networks patched in the same batch.

Quick Summary – TLDR:

  • Palo Alto Networks disclosed 13 vulnerabilities across PAN-OS and Prisma Access Agent, led by the buffer overflow tracked as CVE-2026-0288.
  • The flaw sits in the User-ID Terminal Server Agent (TSA) component, which an unauthenticated attacker with network access can abuse to cause a denial-of-service condition or potentially execute arbitrary code.
  • Seven of the newly patched flaws carry a medium severity rating, per SecurityWeek, including two in Prisma Access Agent that enable man-in-the-middle attacks intercepting VPN traffic and bypassing data-loss-prevention controls.
  • Five vulnerabilities are rated low severity, covering privilege escalation, cross-site-scripting code execution, and firewall-policy bypass.
  • Palo Alto Networks says it is not aware of any malicious exploitation of the issues, and Panorama is not affected.

What Happened?

The bug, CVE-2026-0288, covers multiple buffer overflow vulnerabilities in the User-ID Terminal Server Agent (TSA) component of PAN-OS software, according to Palo Alto Networks. The CVE carries a high severity and the highest urgency rating Palo Alto Networks assigns, the most severe of the 13 flaws in the batch, per SecurityWeek’s tally.

The attack path, per Palo Alto Networks’ own advisory, is direct: a specially crafted network packet sent to a vulnerable TSA-configured firewall can trigger a crash or, in a worse case, arbitrary code execution, with no authentication required. That combination, no login needed, remote network reach, and a code-execution ceiling, is what separates a routine patch from one that belongs on every firewall admin’s list this week.

Palo Alto Networks has disclosed CVE-2026-0288, a critical PAN-OS vulnerability allowing unauthenticated remote code execution via the User-ID Terminal Server Agent. Affected versions include PAN-OS 12.1, 11.2, 11.1, and 10.2. Immediate patching is strongly advised to mitigate… pic.twitter.com/LY0ovc2KGS

— The Daily Tech Feed (@dailytechonx) July 9, 2026

Inside the Buffer Overflow

The bug affects the Terminal Server Agent component of PAN-OS and does not impact Panorama, and firewalls that never enabled TSA, configured under Device > User Identification > Terminal Server Agents, are not exposed. Palo Alto Networks’ own mitigation guidance is specific: restricting TSA connectivity to trusted internal IP addresses, per the company’s recommended deployment guidelines, minimizes the security risk. That configuration change helps reduce exposure; it does not eliminate the underlying bug, which still needs the vendor patch.

Palo Alto Networks is not aware of any malicious exploitation of these issues. the advisory states. Prisma Access customers get a medium-severity version of the same issue and will be upgraded automatically during the next scheduled maintenance window, or sooner on request through Palo Alto Networks Support.

The Other 12 Vulnerabilities

The remaining fixes split into two tiers by impact. Five of the seven medium-severity PAN-OS flaws can be exploited to trigger a denial-of-service condition, execute arbitrary OS commands as root, send unauthorized requests from the firewall to internal services, obtain information, or bypass authentication. With the higher-impact issues among them requiring the attacker to already be authenticated with admin privileges. That authentication requirement is a meaningfully lower bar for attackers than CVE-2026-0288‘s unauthenticated path, since it assumes a foothold already exists, but still a dangerous escalation route once one does.

The other two medium-severity bugs sit in Prisma Access Agent and can be exploited for man-in-the-middle attacks that intercept VPN traffic and bypass data loss prevention policy enforcement, a direct risk to remote work security programs that lean on Prisma Access for off-network staff.

SeverityCountPrimary impact
High1DoS or remote code execution, unauthenticated
Medium7DoS, root command execution, VPN interception, auth bypass
Low5Privilege escalation, XSS, policy bypass, file deletion

The five low-severity vulnerabilities allow privilege escalation, code execution via cross-site scripting attacks, firewall policy bypassing, file deletion, and information disclosure. A security bulletin from Hong Kong’s government-backed computer emergency response team corroborates the scope, listing remote code execution, denial of service, security restriction bypass, cross-site scripting, information disclosure, and data manipulation among the impacts across the affected PAN-OS, Prisma Access, and Cloud NGFW product lines.

Newsletter
Don’t chase tech news. We track it for you.

One weekly briefing with the launches, AI developments, and breaches that matter. No filler.

Who Needs to Patch?

Affected versions span PAN-OS 10.2 in its entirety, PAN-OS 11.1 releases earlier than 11.1.16, and PAN-OS 12.1 releases earlier than 12.1.8, alongside Prisma Access 10.2 (all versions), Prisma Access 11.2 (all versions), Prisma Access 12.1 releases earlier than 12.1.8, and Cloud NGFW on AWS and Azure. Security teams managing small business cybersecurity already know unauthenticated, network-reachable firewall bugs are the pattern threat actors move on fastest once a patch reveals the flaw.

SQ Magazine’s Takeaway

This is a firewall-perimeter patch cycle, not a breach disclosure, and the distinction matters. The Prisma Access Agent bugs are the sleeper risk in the batch: VPN interception and DLP bypass hit organizations that assumed their remote-access layer was the safe side of the network, quietly undercutting the trust model that remote-heavy companies increasingly rely on.

What’s next: firewall admins should confirm whether TSA is configured before treating this batch as urgent, since the headline flaw cannot be triggered on devices where TSA is disabled. Where TSA is active, apply the vendor patch and restrict TSA connectivity to trusted internal IPs in the interim. Prisma Access customers should confirm their scheduled maintenance window or request an on-demand upgrade rather than waiting on the default cycle, and PAN-OS admins should audit which accounts hold firewall admin privileges, since most of the medium-severity bugs require that access to exploit.
This article has been reviewed and fact-checked by Robert A. Lee. SQ Magazine follows strict Publishing Principles and a documented Fact-Check Policy to ensure accuracy, transparency, and editorial independence across all content.

Add SQ Magazine as a Preferred Source on Google for updates! Follow on Google News
Share ChatGPT Perplexity

References

  • CVE-2026-0288 PAN-OS: Buffer Overflow Vulnerabilities in User-ID Terminal Server Agent
  • Palo Alto Products Multiple Vulnerabilities
  • Palo Alto Networks Patches 13 Vulnerabilities
Sofia Ramirez

Sofia Ramirez

Senior Tech Writer


Sofia Ramirez is a technology and cybersecurity writer at SQ Magazine. With a keen eye on emerging threats and innovations, she helps readers stay informed and secure in today’s fast-changing tech landscape. Passionate about making cybersecurity accessible, Sofia blends research-driven analysis with straightforward explanations; so whether you’re a tech professional or a curious reader, her work ensures you’re always one step ahead in the digital world.

Related Posts

Microsoft Bitlocker Rce Patch
Cybersecurity

Critical Windows BitLocker Flaw Sparks Urgent Patch

Papercut Ships Tested Fixes Ai Attacks
Cybersecurity

PaperCut Ships Tested Fixes After AI Agents Breach 395 Organizations

Cisa Warns To Patch Windows Server Wsus Flaw
Cybersecurity

Hackers Exploit WSUS Flaw as Feds Rush to Secure Vulnerable Servers

Disclaimer: The content published on SQ Magazine is for informational and educational purposes only. Please verify details independently before making any important decisions based on our content.

Reader Interactions

Leave a Comment Cancel reply

Primary Sidebar

Connect With Us

facebook x linkedin google-news telegram pinterest whatsapp email
google-preferred-source-badge Add as a preferred source on Google

You Should Also Read

Citrix NetScaler Bug CVE-2026-8452 Exploited in the Wild
Cisco Rushes Hot Fixes as Firewall VPN Flaw Is Exploited
Urgent Check Point VPN Flaws Expose Systems to RCE

Table of Contents

  • Quick Summary – TLDR:
  • What Happened?
  • Inside the Buffer Overflow
  • The Other 12 Vulnerabilities
  • Who Needs to Patch?
  • SQ Magazine’s Takeaway
Connect on Telegram

Footer

SQ Magazine Logo

Smarter Insights for a Fast-Moving Digital World

Connect With Us

Follow Us on Google News

Editorial & Trust

  • About
  • Publishing Principles
  • Fact-Check Policy
  • Corrections Policy
  • Ethics Policy
  • Disclaimer

Worth Checking

  • Social Media Attention Span Stats
  • Gen Z Social Media Statistics
  • TikTok vs. Instagram Statistics
  • LLM Hallucination Statistics
  • Spotify User Statistics
  • Apple Customer Loyalty Statistics
  • Data Breach Tracker
  • Patch Tuesday Dashboard
  • AI Model Tracker
  • AI Funding Tracker
Contact Us
13570 Grove Dr #189,
Maple Grove, MN 55311,
United States
10 a.m. to 6 p.m. | Every day

Copyright © 2022–2026 SQ Magazine. All Rights Reserved. Powered by the Neural Stack.

  • Privacy Policy
  • Terms
  • Accessibility Statement
Company
  • About Us
  • Our Team
  • Our Mission
  • Core Values
Discover
  • Brand Assets
    Brand Assets
  • Stats Methodology
    Stats Research Process
  • Glossary
    Glossary
Categories
  • Internet
  • Technology
  • Artificial Intelligence
  • Gaming
  • Cybersecurity
Internet
How Many Videos Are on YouTube Statistics
How Many Videos Are on YouTube Statistics 2026: Key Data
How Many People Work at WhatsApp
How Many People Work at WhatsApp 2026: Employee Count and History
Spotify Listening Statistics
Spotify Listening Statistics 2026: Average Listening Time
How Many Subscribers Does MrBeast Have
How Many Subscribers Does MrBeast Have in 2026? Channel Growth Statistics
WhatsApp Business Statistics
WhatsApp Business Statistics 2026: Real Market Insights
Udemy Statistics
Udemy Statistics 2026: Revenue and Learner Data
Technology
Aptoide Statistics 2026: Downloads, Users and App Store Share
AppsFlyer Statistics Customers Revenue and Market Position
AppsFlyer Statistics 2026: Customers, Revenue and Market Position
How Many iPhones Has Apple Sold
How Many iPhones Has Apple Sold in 2026? Units Sold by Year
How Many Employees Does Amazon Have
How Many Employees Does Amazon Have 2026: Workforce Growth
Netflix vs. Hulu Statistics
Netflix vs Hulu Statistics 2026: Viewer Growth Data
TripAdvisor Statistics
TripAdvisor Statistics 2026: Revenue, Reviews, Viator and TheFork Data
Artificial Intelligence
AI Search Engine Statistics Usage Market Share and Adoption
AI Search Engine Statistics 2026: Usage, Market Share and Adoption
AI Music Statistics
AI Music Statistics 2026: Generation, Adoption and Industry Impact
AI Coding Statistics
AI Coding Statistics 2026: Adoption, Productivity and Market Data
How Much Content on Social Media Is AI Generated Statistics
How Much Content on Social Media Is AI Generated Statistics 2026: Hidden Truths
ChatGPT vs DeepSeek Statistics
ChatGPT vs DeepSeek Statistics 2026: Users, Benchmarks & Pricing
ChatGPT vs Claude vs Gemini vs Perplexity Statistics
ChatGPT vs Claude vs Gemini vs Perplexity Statistics 2026: Users, Revenue & Market Share
Gaming
Gaming Statistics
Gaming Statistics 2026: Market Size, Players, Revenue, and Platforms
Roblox vs Minecraft Statistics
Roblox vs Minecraft Statistics 2026: Players, Revenue, Creators
Online Gambling Regulations Statistics
Online Gambling Regulations Statistics 2026: Global Compliance and Enforcement Data
Fantasy Sports Statistics
Fantasy Sports Statistics 2026: Users, Revenue & Trends
Apex Legends Statistics 2026: Players, Revenue, and Esports
Fortnite Statistics
Fortnite Statistics 2026: Players, Revenue, Esports, and Engagement
Cybersecurity
Signal Statistics
Signal Statistics 2026: Users, Finances and Encryption Adoption
Password Statistics
Password Statistics 2026: Credential Theft, MFA, and the Passkey Tipping Point
Identity Theft Statistics
Identity Theft Statistics 2026: Key Fraud Data and Trends
CVE Statistics
CVE Statistics 2026: Severity Distribution and Top Affected Vendors
Dark Web AI Tool Marketplace Statistics
Dark Web AI Tool Marketplace Statistics 2026: Explosive Market Growth
API Security Breach Statistics
API Security Breach Statistics 2026: Hidden Threats
Categories
  • Cybersecurity
  • Artificial Intelligence
  • Internet
  • Technology
  • Gaming
Cybersecurity
Arista Velocloud Flaw Patched
Arista VeloCloud Flaw Hits CVSS 10.0: Patch Now
Microsoft Takes Down Eviltokens Ai Phishing Service
Microsoft Takes Down EvilTokens AI Phishing Service
Microsoft Patches Azure Ai Foundry Cvss 10 Flaw Featured 1
Microsoft Patches 18 Azure and Copilot Security Vulnerabilities
Chatgpt Billing Phishing Scam Active
ChatGPT Billing Scam Exposes Critical OpenAI Account Risk
Gyazo Data Breach Image Metadata Leak
Gyazo Breach Exposes Link IDs Behind Private Captures
Spain Aepd Ai Assisted Cyberattack
Spain’s AEPD Logs First Data Breach Caused by AI Agent
Artificial Intelligence
Youtube Music Ask Music Ai Feature
YouTube Music Adds Smart AI Features for Songs and Podcasts
OpenAI Launches GPT-6 Sol and Luna at Half the API Price
Claude Opus 5 5 Launched
Claude Opus 5.5 Debuts With Powerful Cyber Defenses
xAI Launches Grok 4 7 Its Most Capable Coding Model Yet
xAI Launches Grok 4.7, Its Most Capable Coding Model Yet
Perplexity Computer Model Effort Control
Perplexity Computer Adds Powerful Effort Controls for Model Selection
Anthropic Merges Claude Chat And Cowork
Anthropic Merges Claude Chat and Cowork Into One Window
Internet
Meta Launched Meta One Subscription
Meta One Bundles Instagram, Facebook, WhatsApp Into One AI Subscription
Apple Wallet Ids Launch In Oklahoma
Apple Wallet IDs Launch in Oklahoma in Major Expansion
Meta to Pay 18 Billion in Landmark Teen Safety Deal
Meta to Pay $18 Billion in Landmark Teen Safety Deal
Whatsapp Brings Passkeys 2fa
WhatsApp Hits 1 Billion Passkey Users, Adds 2FA Passwords
Apple Eu App Store Fee Reduction
Apple Sets New EU App Store Fees, Effective October 1
Github Outage Aug 2026
GitHub Down: Outage Hits Thousands of Users Worldwide
Technology
Youtube Custom Feeds With Gemini Ai
YouTube’s AI Feed Builder Changes Video Discovery
Iphone 18 Pro Face Id Bug Reboot Crash
New iPhone 18 Pro Bug Makes Face ID Crash and Reboot
Googlebook With Gemini Ai Launched
Googlebook’s Bold Laptop Launch Starts at $899 in the US
New Samsung Patent Reveals Galaxy Watch Glucose Tracking
Microsoft Kb5002914 Breaks Excel Copypaste
Microsoft Confirms KB5002914 Breaks Excel Copy and Paste
Homepod 27 Update Launched By Apple
Apple Releases HomePod Software 27 With AutoMix Support
Gaming
Xbox Live Down Again
Xbox Live Down Again: Sign-In Error 0x80004005 Hits Players
Gta Vi Official Cover Art
GTA 6 Pre-Orders Start June 25, New Cover Art Unveiled
Epic Games Teases Unreal Engine 6 For Rocket League
Epic Games Teases Unreal Engine 6 for Rocket League
Stardew Valley Launched For Nintendo Switch 2 Edition
Stardew Valley Switch 2 Edition Arrives with Online Co-op
Hogwarts Legacy Game Crosses 40m Downloads
Hogwarts Legacy Crosses 40M Sales, Beating Industry Giants
Pubg Black Budget Closed Alpha Launched
PUBG: Black Budget Launches Closed Alpha Test With a Bold PvPvE Twist
Newsletter

Too much tech noise?

We respect your time. One high-signal briefing a week: tech, AI, and security. Nothing else.

Newsletter

The SQ Briefing

We track tech, AI, and security 24/7. You get a 5-minute weekly summary.